 Cyber Attack
SOGo Groupware Proxy Authentication Flaw Allows Unauthenticated Account Impersonation via WebObjects Header (CVE-2026-74864)
Cyber AttackCloud & SaaSCVE-2026-74864
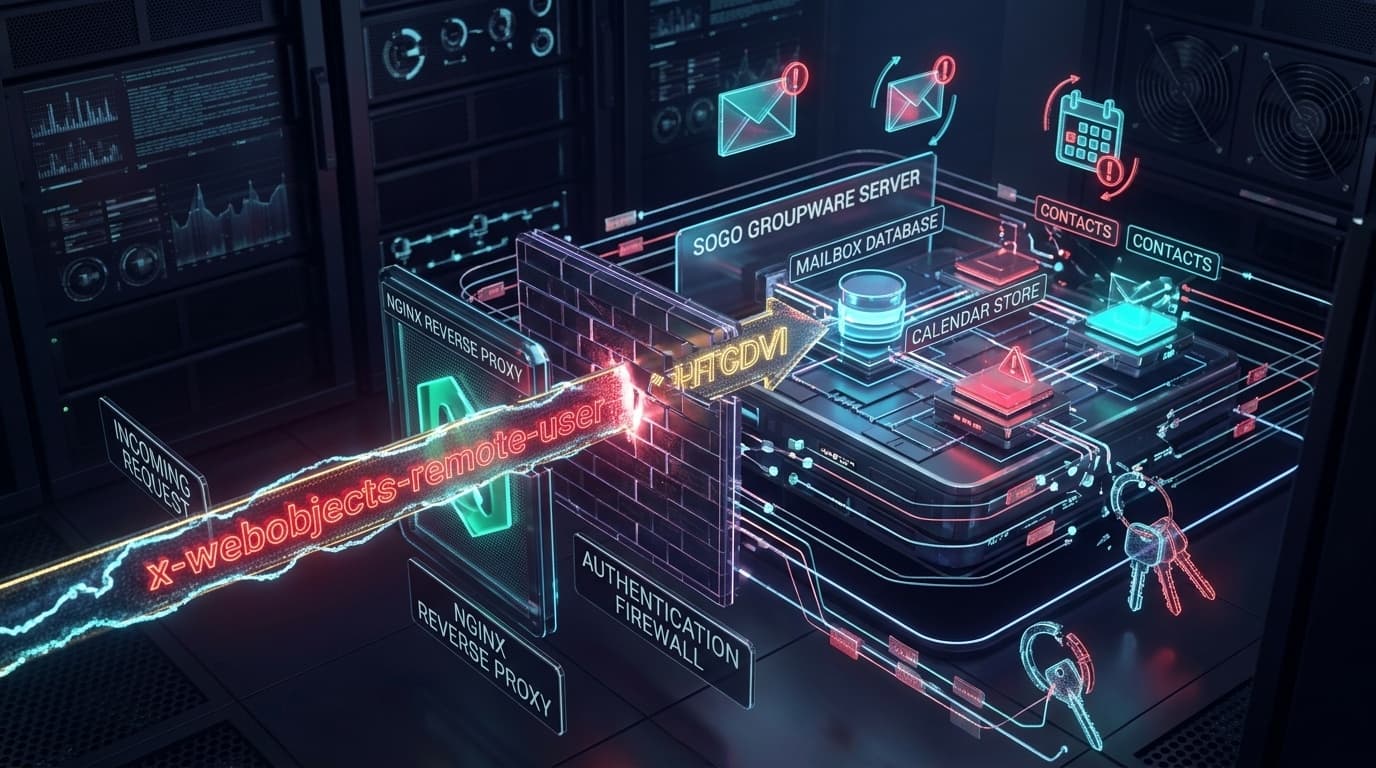
An authentication bypass in SOGo groupware allows remote attackers to impersonate any user without credentials by supplying an unsanitized x-webobjects-remote-user header.
CST Editorial Desk11 min read