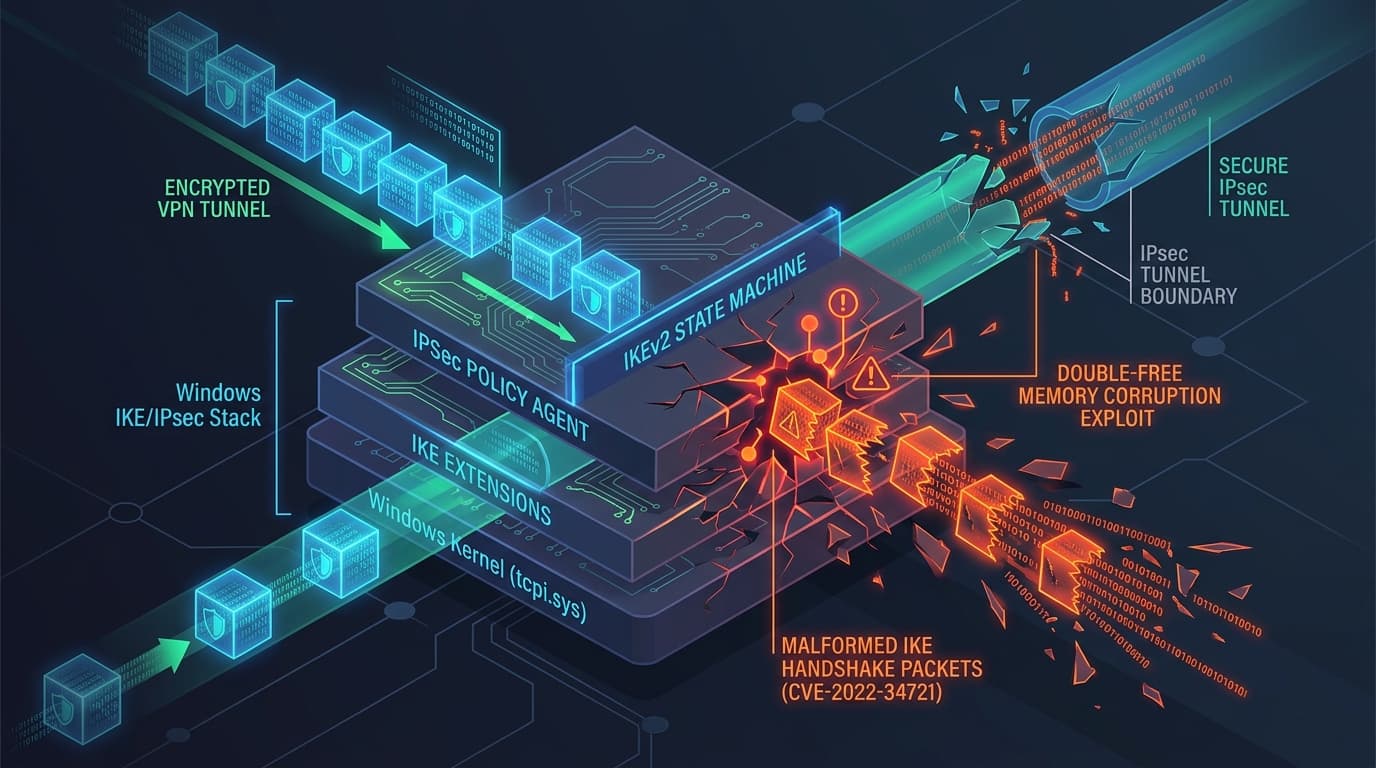
ThreatsTechnology, Cloud & SaaSBreakingMicrosoft Windows IKE Protocol Double-Free Flaw CVE-2026-33824 Added to CISA KEV Under Active In-the-Wild ExploitationCISA confirms active in-the-wild exploitation of CVE-2026-33824, an unauthenticated double-free memory corruption flaw in Windows IKE enabling remote root code execution over UDP 500.Mei-Lin Chen·15 Sep 2026, 12:00 IST·8 min read