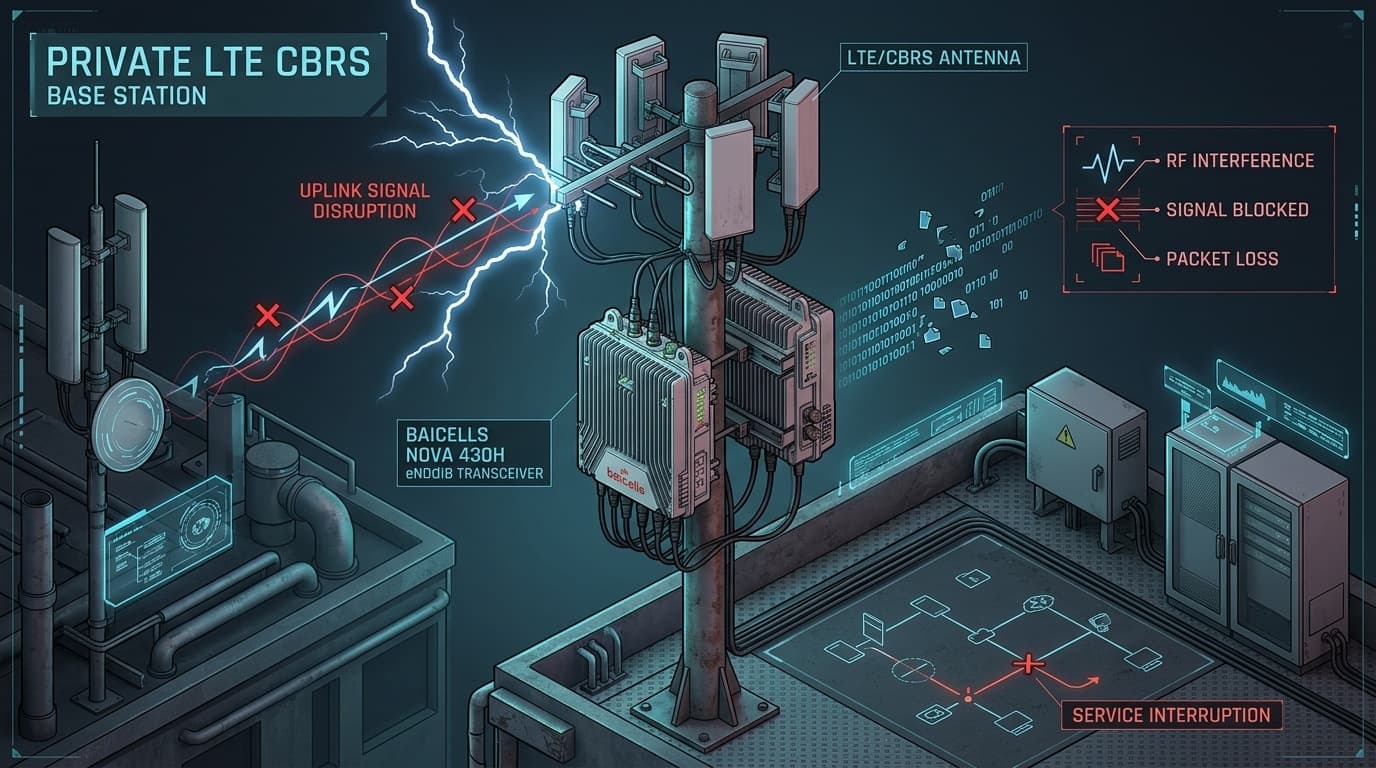
The Cybersecurity and Infrastructure Security Agency (CISA) has issued security advisory ICSA-26-272-04 warning industrial asset owners of a high-severity denial-of-service vulnerability (CVE-2026-96274, CVSS 7.5) impacting Baicells Nova 430H outdoor micro-eNodeB base stations. The devices, deployed across automated container shipping terminals, open-pit mines, and electrical utility grids to provide private Citizens Broadband Radio Service (CBRS) and LTE wireless backhaul, can be knocked offline by unauthenticated attackers transmitting malformed radio frequency (RF) uplink packets.
Private Cellular in Industrial Automation (IACS)
In modern critical infrastructure, industrial private LTE/5G networks have largely superseded commercial Wi-Fi due to superior range, deterministic latency, and support for high-speed automated machinery. The Baicells Nova 430H serves as a compact 4x250mW outdoor transceiver connecting automated guided vehicles (AGVs), autonomous haulage trucks, and remote terminal units (RTUs) to the industrial core network (EPC).
Vulnerability Mechanics: SCTP Signaling Teardown (CWE-20)
The vulnerability resides within the LTE Layer 3 Radio Resource Control (RRC) and Stream Control Transmission Protocol (SCTP) signaling parser.
When processing incoming uplink control frames from mobile client stations, the eNodeB firmware fails to validate the structure of specific RRC connection request parameters. An unauthenticated adversary operating a software-defined radio (SDR) within RF transmission range can broadcast malformed signaling frames:
# Threat actor transmission via Software-Defined Radio (SDR)
Transmitted Frame: LTE Uplink RRCConnectionRequest
Malformed Parameter: IE-EstablishmentCause (Invalid Bit Length 0xFF)
Result: Kernel panic in baseband processor -> SCTP S1-MME Link Teardown
The malformed frame causes the baseband processing software to crash, terminating the SCTP association between the eNodeB and the Mobility Management Entity (MME). All connected industrial clients lose connectivity instantaneously, triggering emergency safety shutdowns across autonomous robotic machinery.
Mitigation Actions for Private Network Operators
- Deploy Baicells Firmware Patch: Contact Baicells technical support to deploy the latest firmware update incorporating boundary validation for all RRC signaling parameters.
- Deploy Radio Frequency Intrusion Detection (RFID): Install RF spectrum monitoring sensors around perimeter boundaries to identify unauthorized SDR transmissions or rogue LTE cell spoofing.
- Fail-Safe Physical Interlocks: Ensure that all autonomous machinery and remote RTUs utilize independent hardware fail-safe mechanisms when cellular carrier signals drop, preventing runaway mechanical conditions.
Vulnerable Software Versions & Patch Status Matrix
| Hardware / Firmware Model | Vulnerable Firmware Versions | Fixed / Remediated Release | Remediation Action Required |
|---|---|---|---|
| Baicells Nova 430H Outdoor eNodeB | Firmware < BaiBS_RTS_3.7.11 | BaiBS_RTS_3.7.11 | Apply firmware update via OMCI / Web GUI and reboot eNodeB |
| Baicells Nova 227 / 233 Private LTE | Firmware < BaiBS_RTS_3.7.11 | BaiBS_RTS_3.7.11 | Verify management VLAN isolation and flash firmware |
Step-by-Step Firmware Upgrade & Radio Hardening Commands
Telecom field engineers must verify active firmware and isolate management interfaces:
# Connect via administrative CLI to Baicells eNodeB
ssh admin@192.168.150.1

# Query current running firmware version
show version
# Expected: Software Version BaiBS_RTS_3.7.11 or higher

# Apply firmware upgrade package via remote FTP/TFTP server
upgrade firmware tftp://10.10.20.5/BaiBS_RTS_3.7.11.bin

# Verify radio carrier status and S1-MME link stability
show cell status