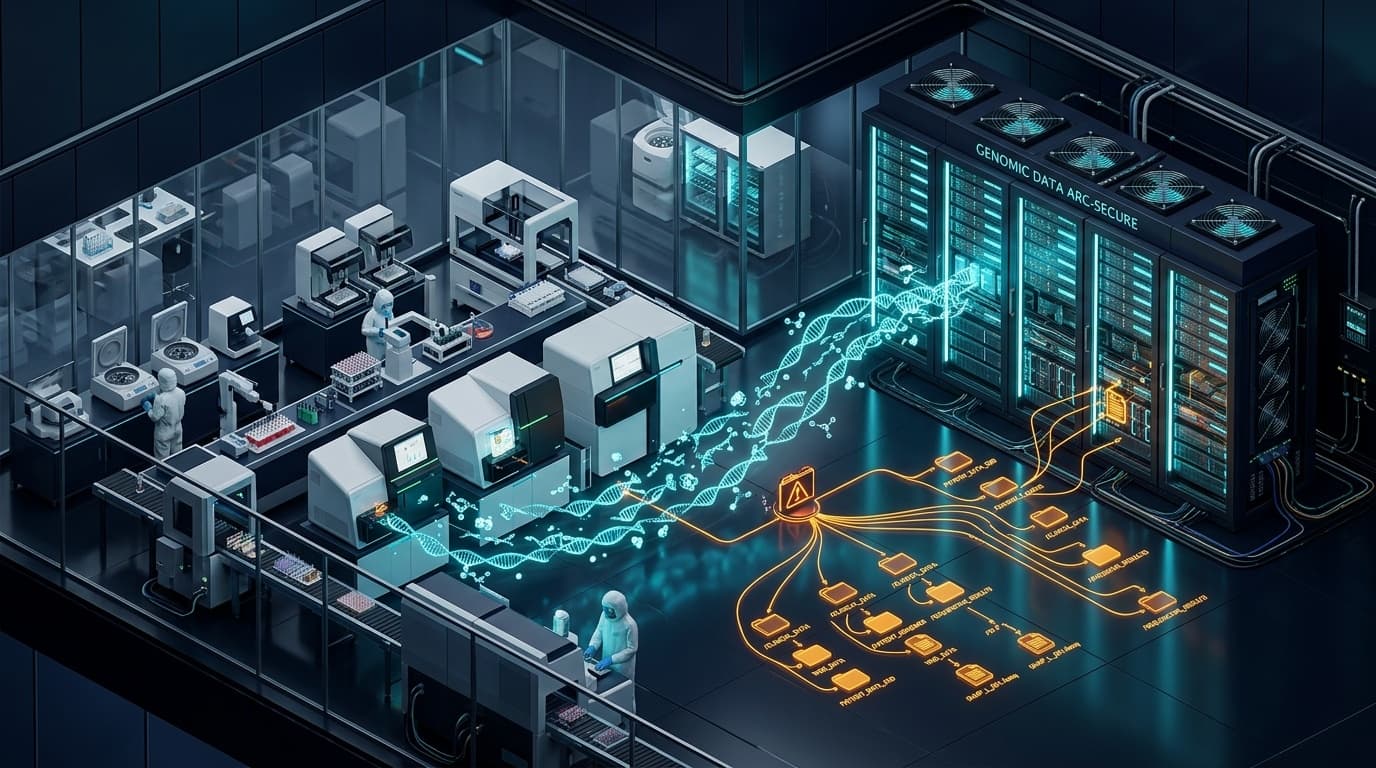
The Cybersecurity and Infrastructure Security Agency (CISA) has released an industrial medical advisory, ICSMA-26-288-01, warning of a path traversal vulnerability tracked as CVE-2026-107777 in Thermo Fisher Scientific Torrent Suite Software. The application coordinates raw signal acquisition, base calling, and secondary variant analysis for Ion Torrent next-generation sequencing (NGS) platforms deployed across clinical diagnostics laboratories, pharmaceutical development pipelines, and public health sequencing centers worldwide.
Path Traversal Vulnerability & Sequencing Data Exposure
Torrent Suite Software operates as an integrated Linux server application paired directly with Ion GeneStudio, Ion Proton, and Ion PGM sequencing instruments. It provides lab technicians and bioinformaticians with a web-based dashboard to configure sequencing runs, monitor instrument telemetry, and download raw sequencing output files (FASTQ, BAM, and VCF files).
The vulnerability, classified as CWE-22 (Improper Limitation of a Pathname to a Restricted Directory), resides in the HTTP file export and log viewing API handler. The web service endpoint accepts file path parameters without stripping relative directory traversal sequences (such as ../ or URL-encoded equivalents like %2e%2e%2f). An authenticated user possessing basic technician-level credentials can traverse outside the designated web root and access any file on the underlying operating system accessible to the web server process:
/* Conceptual representation of path traversal request targeting Torrent Server */
GET /rundb/api/v1/download?file=../../../../../../etc/shadow HTTP/1.1
Host: torrent-server.lab.internal
Authorization: Basic [Technician-Credentials]
Accept: application/octet-stream
While exploiting the defect requires valid user credentials, laboratory environments frequently share generic technician logins across shift workers or operate with default administrative passwords. A compromised technician credential allows threat actors to exfiltrate critical clinical and operational assets:
- Patient Genomic Data & Variant Calls: Unencrypted VCF and BAM alignment files containing sensitive germline and somatic genetic profiles subject to HIPAA and GDPR health privacy protections.
- Proprietary Assay Chemistry: Proprietary primer pool designs, sequencing bead chemistry profiles, and patent-sensitive target enrichment workflows.
- System Credentials & SSH Keys: Server configuration files, database connection strings (PostgreSQL), and private cryptographic keys used to secure instrument communication conduits.
Severity Metrics & Affected Software Versions
| Metric / Evaluation | Vulnerability Detail |
|---|---|
| Advisory Reference | CISA ICSMA-26-288-01 / ICS Medical Advisory |
| CVE Identifier | CVE-2026-107777 |
| CVSS v4.0 Score | 7.1 (High): CVSS:4.0/AV:N/AC:L/AT:N/PR:L/UI:N/VC:H/VI:N/VA:N/SC:N/SI:N/SA:N |
| CVSS v3.1 Score | 6.5 (Medium): CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N |
| Affected Product Releases | Torrent Suite Software versions 5.18 and prior |
| Remediated Release | Torrent Suite Software version 5.22 or later |
Healthcare & Clinical OT Defense Recommendations
CISA and Thermo Fisher Scientific recommend that hospital networks, clinical research institutes, and commercial genomics labs implement the following defensive controls:
- Update to Torrent Suite Software 5.22: Contact Thermo Fisher technical support or access the customer portal to download and apply Torrent Suite Software version 5.22, which enforces strict canonical path sanitization across all API endpoints.
- Enforce Purdue Model Network Segmentation: Isolate next-generation sequencing instruments and Torrent Suite servers within a dedicated Laboratory Information Management System (LIMS) VLAN. Never expose sequencing servers directly to the public internet or broad corporate office subnets.
- Enforce Individual Named Accounts: Eliminate shared laboratory logins; require every bioinformatician and laboratory technician to use unique credentials protected by multi-factor authentication.
- Audit Operating System Permissions: Ensure the Linux service account running the Torrent Suite web daemon has minimal filesystem permissions, with read access denied to sensitive system directories (
/etc/shadow,/root/).