 OT / SCADA
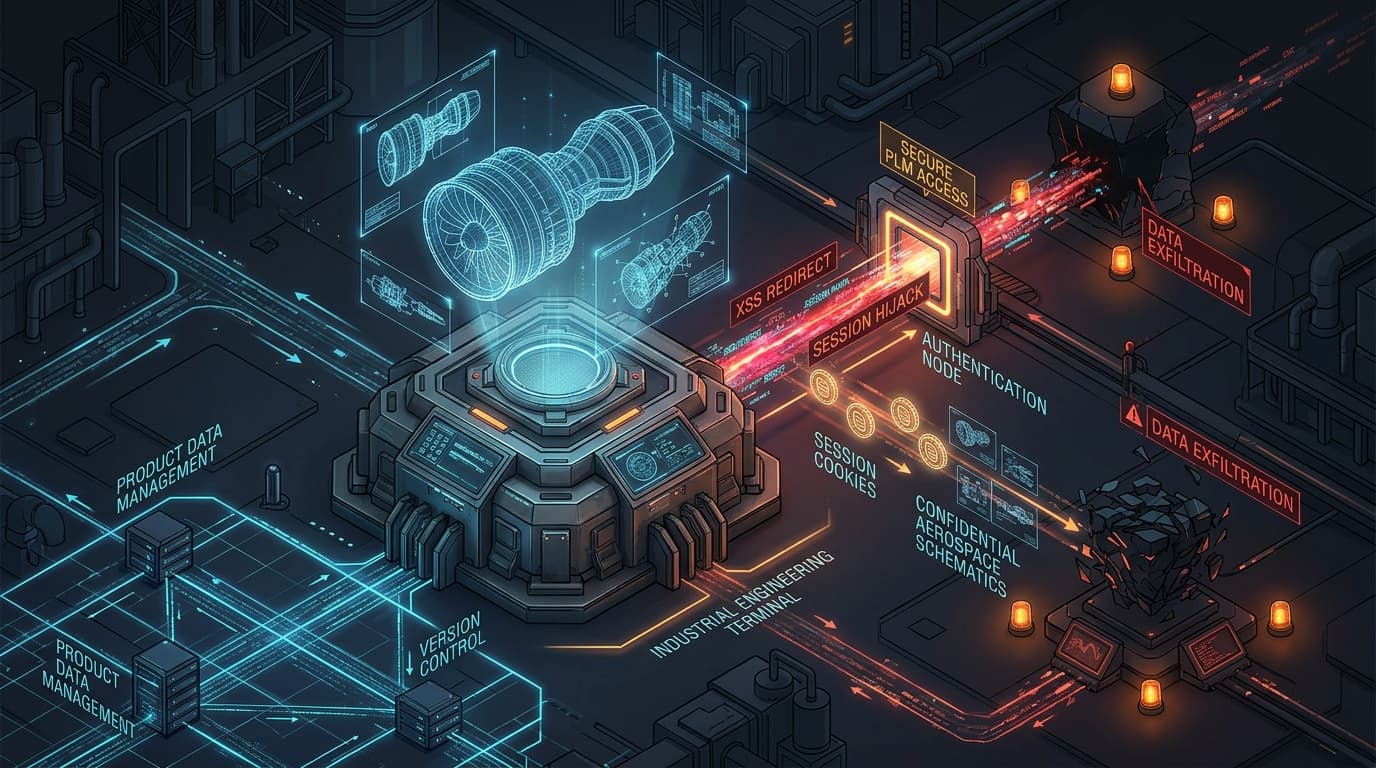
Siemens Teamcenter Authentication Redirect Flaw Exposes Industrial PLM Blueprints to Session Hijacking CVE-2026-58113
ThreatsIndustrial & OTCVE-2026-58113High
Siemens and CISA issue advisory ICSA-26-258-07 for CVE-2026-58113 in Teamcenter PLM, where reflected XSS in authentication redirects allows remote attackers to hijack CAD sessions.
CST Editorial Desk15 min read