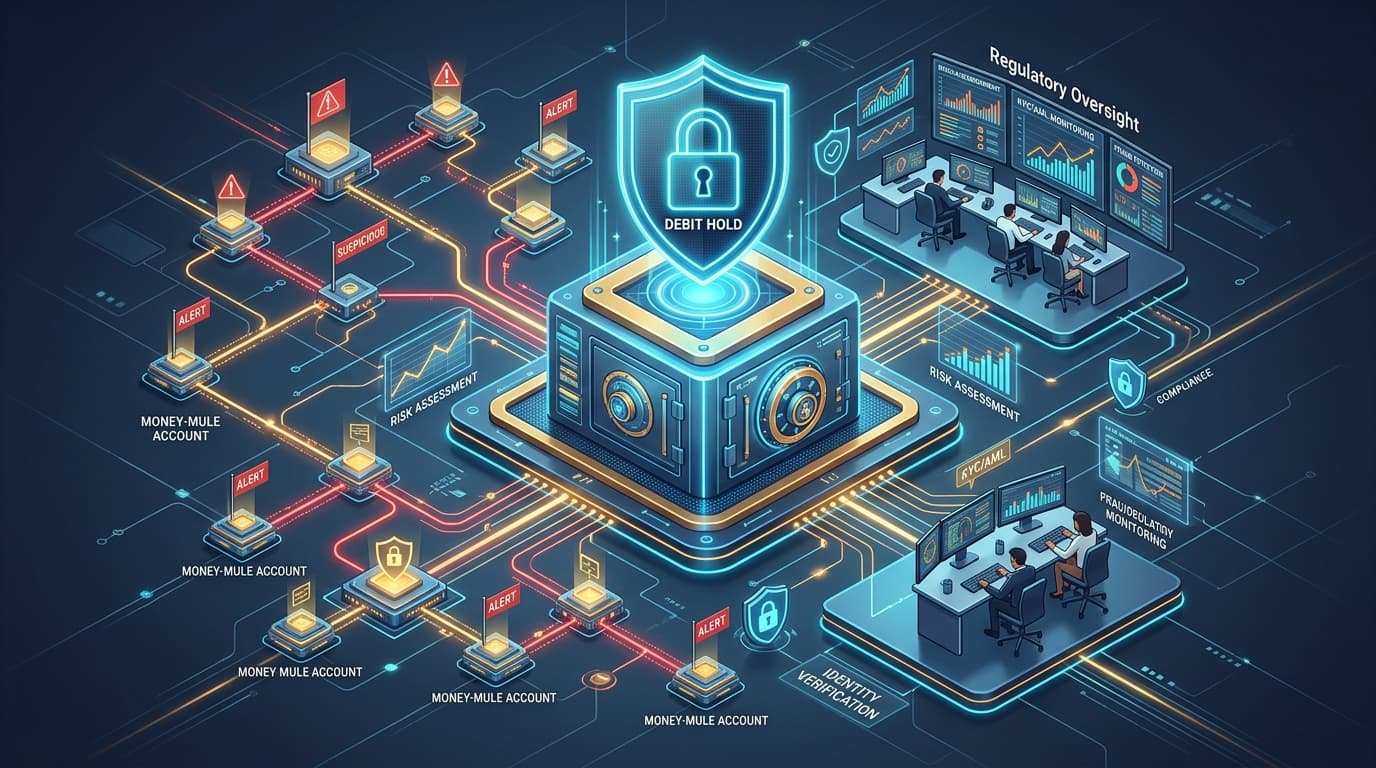
Deep DiveRBI drafts a time-bound debit-hold SOP for suspected money-mule accounts
RBI’s draft KYC amendment proposes a time-bound process for temporary debit holds on suspected money-mule accounts linked to cyber-enabled fraud.
206 articles
Deep DiveRBI’s draft KYC amendment proposes a time-bound process for temporary debit holds on suspected money-mule accounts linked to cyber-enabled fraud.
GoogleThreatFabric uncovers StreamRAT, a sophisticated Android banking trojan promoted via fraudulent Meta TV streaming ads, hijacking Accessibility services to drain accounts.
MicrosoftMicrosoft retires SMS and voice MFA on 1 February 2027 with a blocking passkey prompt and no opt-out. Here is a dated plan for service accounts, break-glass and phoneless users.
Gov / DefenseIndia's six-hour CERT-In reporting clock has run since June 2022. From May 2027 a second DPDP clock starts on the same incident. Build one intake process now.
GoogleGroup-IB uncovered a major evolution in the Gigabud banking trojan, which uses Android enterprise Work Profiles to isolate tampered banking apps and blind client security checks.
Agentic AIPrompt injection is now OWASP’s top LLM risk with reported success rates of 50–84%. Organisations are shipping agents into production well ahead of their controls.
LinuxSAP and Onapsis disclosed OVERPASS (CVE-2026-44756), a maximum-severity kernel flaw in Extended Passport processing enabling unauthenticated root RCE on enterprise ERP hosts.
Agentic AIGravitee says 88% of organisations had a confirmed or suspected AI agent incident, while 82% of executives trust their policy. Both figures, one population.
CrowdStrikeCrowdStrike revealed Slim Spider, a financially motivated cybercrime group abusing cloud IMDS credentials to penetrate Brazilian instant payment (Pix) and crypto custody systems.
Crypto / Web3A vulnerability in the Elements sidechain protocol led to an unauthorized 4,000 BTC withdrawal from the Liquid Federation multi-sig peg, prompting an emergency network freeze and partial fund recovery.
Deep DiveWith 99% of SaaS compromises originating at the identity provider, MFA is no longer the control organisations think they bought. Here is what changed.
Threat IntelResearchers logged 7.4 million infected devices between January and June 2026 — a 27% jump — as the infostealer market matured into a fully automated criminal supply chain.
Deep DivePublic companies must disclose material cyber incidents within four business days. The deadline is simple; deciding what counts as material is not.
Adversary-in-the-middle phishing now defeats standard MFA at industrial scale. Microsoft tracked a single April 2026 campaign spanning 26 countries in 72 hours.