 Threat Intel
Anthropic Model Context Protocol Server Flaw Enables Host Directory Traversal and Unauthenticated Tool Injection (CVE-2026-70114)
ThreatsCloud & SaaSCVE-2026-70114Critical
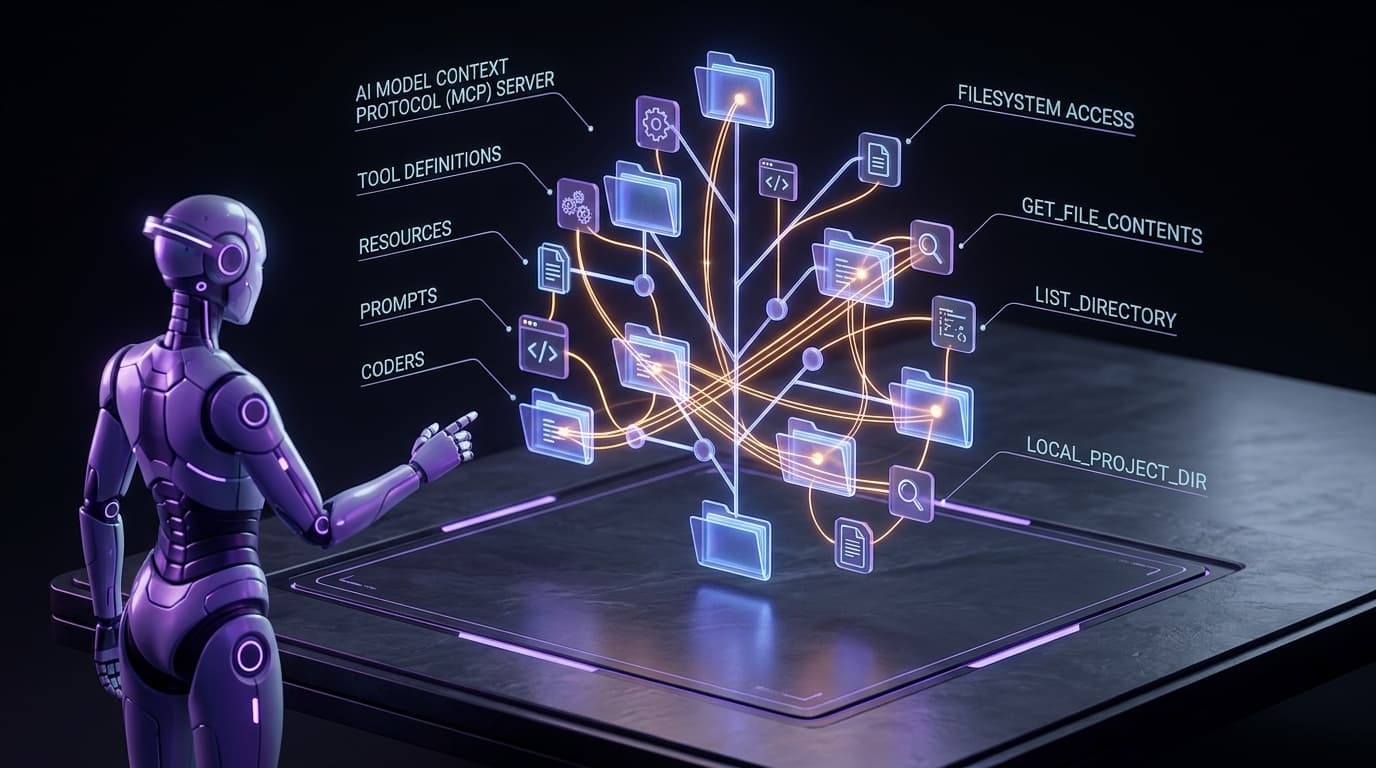
Anthropic issues advisory CVE-2026-70114 for the Model Context Protocol (MCP) filesystem server, patching a path traversal flaw that allowed tool-calling escapes.
CST Editorial Desk8 min read