Executive Summary
Siemens ProductCERT and the Cybersecurity and Infrastructure Security Agency (CISA) have released joint industrial security advisories warning of a critical authentication bypass vulnerability in Siemens SIMATIC WinCC Open Architecture (OA). The vulnerability, designated CVE-2026-51982, carries a CVSS v3.1 base score of 9.8 (Critical) and affects industrial human-machine interface (HMI) and supervisory control architectures globally.
SIMATIC WinCC OA is widely deployed in large-scale mission-critical environments, including municipal drinking water treatment, electrical transmission grids, high-speed rail signalling, and semiconductor fabrication facilities. Successful exploitation allows an unauthenticated network attacker to forge administrative session tokens and override critical process setpoints without alerting plant operators.
Root Cause Analysis: Session Token Entropy Collapse
The root cause lies in the session verification routine implemented within the WCCILpmon process monitoring daemon and the integrated web server component. When validating client requests against the internal token table, the server uses a pseudo-random seed derived solely from the server's uptime timestamp and process ID. Because these values can be deterministically calculated or brute-forced via external timing analysis, an attacker can synthesize valid administrative operator cookies.
Attack Vector Breakdown:
1. Attacker sends synchronization probe to WinCC OA Web Server port 443/5678.
2. Server response reveals high-resolution boot uptime in HTTP headers.
3. Attacker computes session token seed using linear feedback algorithm.
4. Forged admin session token is submitted via HTTP/REST Management API.
5. WinCC OA grants full operator rights to modify process data points.
Industrial Impact & Operational Risk
In an industrial OT context conforming to the Purdue Enterprise Reference Architecture (PERA), WinCC OA typically resides at Level 3 (Site Operations) and interfaces directly with Level 2 (Supervisory Control) and Level 1 programmable logic controllers (PLCs). An unauthorized session compromise at this tier allows attackers to:
- Alter safety interlock thresholds and alarm thresholds.
- Inject false telemetry readings to HMI operator consoles while masking malicious command sequences.
- Force arbitrary PLC stops or disconnect remote terminal units (RTUs) across distributed substations.
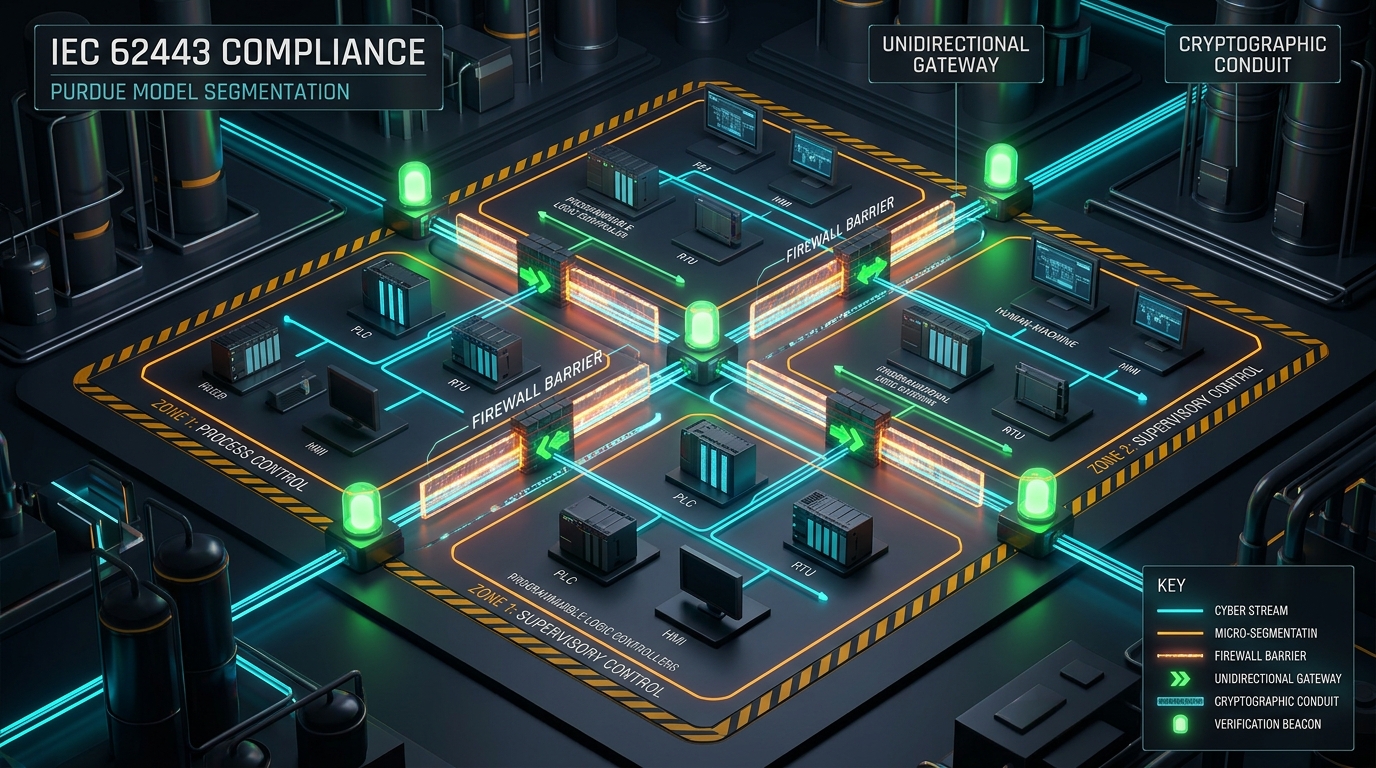
Defensive Guidance & IEC 62443 Zone Segmentation
Siemens has released official security patches and urges all operators to implement defense-in-depth measures in accordance with IEC 62443-3-3 (System Security Requirements):
- Apply Siemens Security Patch: Upgrade SIMATIC WinCC OA v3.19 installations to Patch 4 or higher. For v3.18 environments, apply Cumulative Patch Set 12.
- Zone Boundary Isolation: Enforce strict firewalled boundaries between Enterprise IT (Level 4/5) and the SCADA control network (Level 3). Disable direct web interface exposure to any untrusted network segment.
- Mandatory Mutual TLS (mTLS): Enforce client certificate validation for all remote operator workstations connecting to the WinCC OA web server.
Patch Verification Table
| Product Family | Vulnerable Version | Remediation Release | Action Required |
|---|---|---|---|
| SIMATIC WinCC OA v3.19 | All versions < Patch 4 | v3.19 Patch 4 | Install official Siemens hotfix |
| SIMATIC WinCC OA v3.18 | All versions < P012 | v3.18 Patch 12 | Upgrade to supported maintenance release |