Japanese customer-experience platform provider Plaid has confirmed that an intrusion into its KARTE service exposed 79,249 registered account email addresses, credentials used to connect KARTE to other services, and a portion of data supplied by client companies. The company disclosed the confirmed categories on November 16 and said in a November 18 update that it was still determining which customers and records were affected. The number of exposed emails is established; a total count for the other categories is not.
How the incident unfolded
According to Plaid's company notice, a third party exploited a vulnerability in its servers in the early hours of November 13. The intruder stole credentials used to connect to systems and databases, read data out of databases, and used stolen credentials to take over a company account and access an administrative interface. Plaid says it detected the unauthorized activity at 8:59 a.m. that day. It invalidated stolen credentials, blocked traffic from the attack source, and began stopping servers at about 2:27 p.m. as it moved KARTE services into maintenance mode. The company says these containment actions were complete by about 3:23 p.m.
Plaid said it had not observed fresh unauthorized access after blocking the attacker, while emphasizing that its scope investigation was continuing. That is a statement about what it had detected, not a guarantee that every downstream consequence was known. Its November 18 update said the company was sending affected client companies the imported data identified so far on request and was still working out how to identify and notify the people represented in those records. At that update, it had not announced a timetable for restarting KARTE.
What Plaid says was exposed
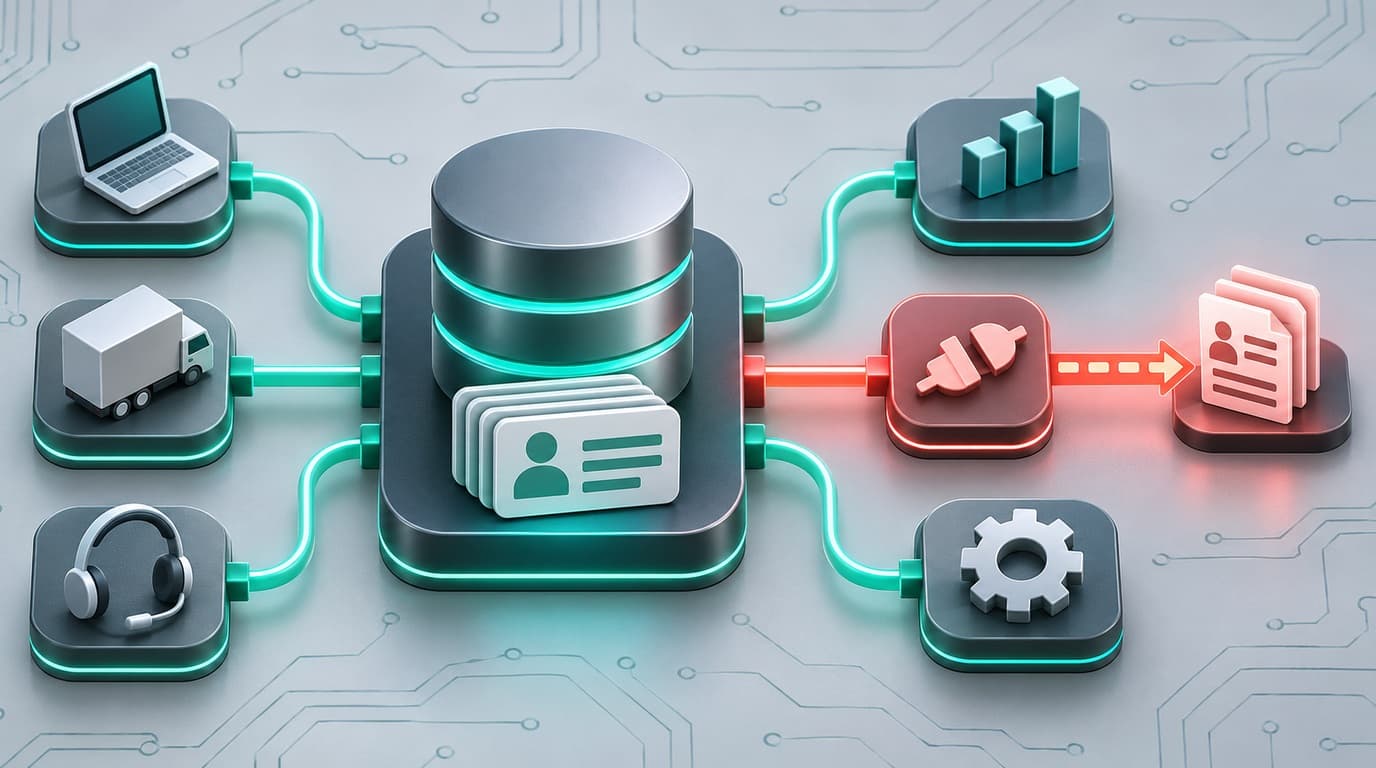
The first confirmed category is 79,249 email addresses registered as KARTE accounts. The second is authentication material used for integrations with outside services, including secret keys and access tokens for customers that configured those connections. Plaid had not established a count for the affected credentials in its November 16 notice. The third category is some data that client companies imported into KARTE to use alongside their own customer information, including data in its linking-table feature. Because each client chooses what fields to import, Plaid says some of those records may contain personal information. The volume and exact data fields remain under investigation.
| Data category | Confirmed status | What remains unknown |
|---|---|---|
| KARTE account email addresses | 79,249 exposed | Individual downstream misuse |
| External-service integration secrets and tokens | Exposure confirmed for configured integrations | Number of affected credentials |
| Client-imported customer data | Some records exposed | Full record count, fields and affected people |
The categories have different consequences. An email address can be used for convincing impersonation or targeted phishing. A live integration token may permit access to a connected service until revoked, depending on that service's permissions. Imported records could contain client-specific personal information, but Plaid has not published a universal field list or a total number of affected individuals. Treating the 79,249 email count as the full breach size would therefore misstate the disclosure.
What customers should do now
Plaid has asked customers using integrations between KARTE and external services to invalidate the relevant connection credentials, especially if they have already received individual notice from the company. This is the immediate control most directly tied to the confirmed exposure: changing a KARTE login password alone will not necessarily revoke an API token or secret held by an integration. Administrators should identify which connected systems use KARTE-issued or KARTE-stored credentials, rotate those secrets at the issuing service, update approved integrations, and review the connected services' access logs for activity outside expected patterns. The precise steps will vary by provider.
Plaid also warned that messages impersonating the company may arrive at KARTE-registered email addresses. Customers should use the company's official notice page and existing support channels to verify requests, rather than following links or attachments in unexpected messages. Organizations that loaded customer records into KARTE should preserve their own mapping of imported fields and await Plaid's individualized scope information before making claims to their users about particular data elements.
The unanswered questions
The disclosure does not name the exploited server vulnerability or publish an attacker's identity. It does not establish the final number of exposed integration secrets or customer records. Plaid says it is contacting affected client companies individually, reporting to Japan's Personal Information Protection Commission, consulting police, and arranging external forensic support. Its subsequent status updates should be read alongside the November 16 disclosure because the impact assessment and service-restoration work are still moving.
For defenders, the broader lesson is concrete: a customer-data platform can act as both a store of personal data and a hub of credentials to other systems. The confirmed facts support immediate credential revocation and careful downstream log review, while the still-open scope questions require measured communication rather than an invented total breach count.