Executive Summary
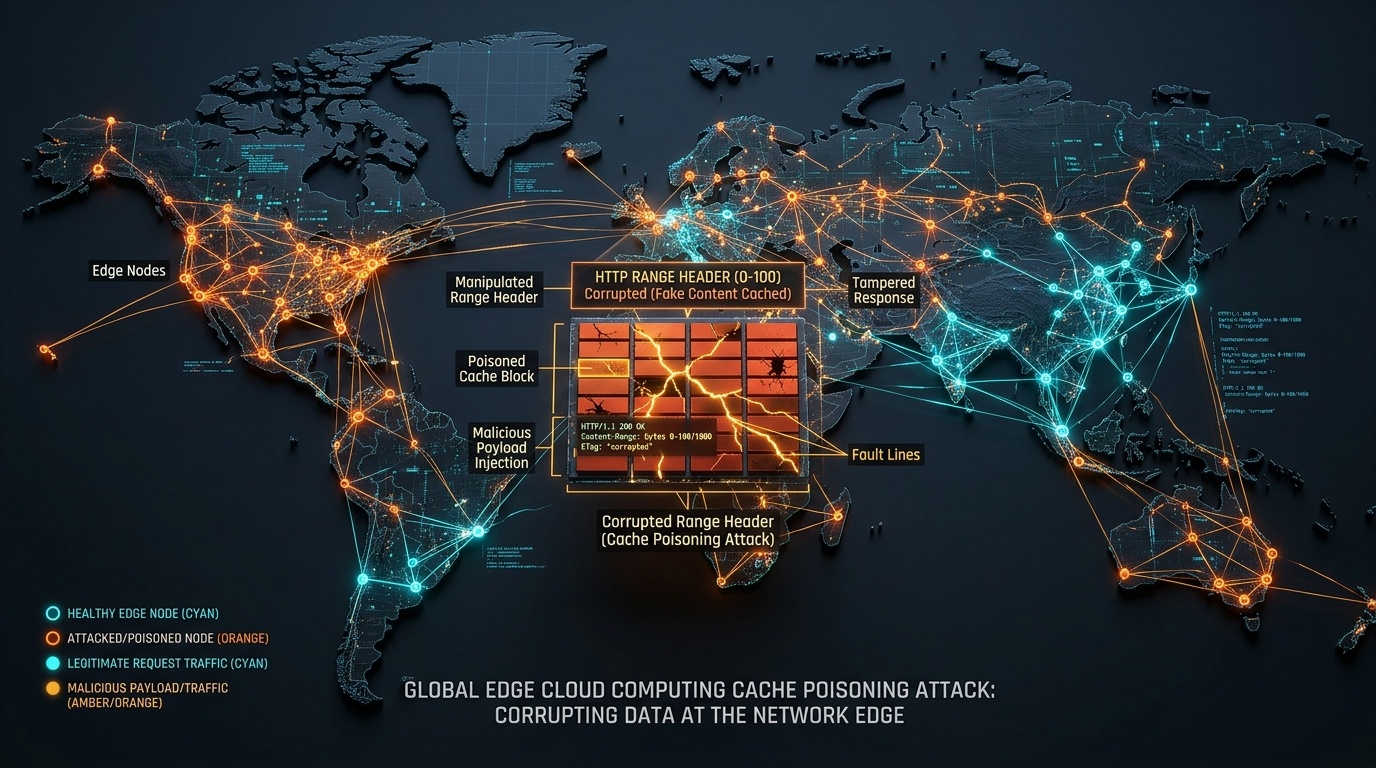
Cloudflare has released a security advisory and deployed global edge infrastructure remediations for CVE-2026-73190, a critical cache poisoning and content desynchronization vulnerability affecting Cloudflare Workers KV and edge caching proxies. Rated with a CVSS v3.1 score of 9.3 (Critical), the vulnerability allowed remote adversaries to exploit edge HTTP Range header parsing discrepancies, permanently injecting attacker-crafted responses into shared CDN edge cache storage.
Cloudflare Workers KV operates across more than 330 cities globally, serving as the high-speed data store for serverless applications, frontend single-page application (SPA) bundles, and dynamic API responses. Exploitation of CVE-2026-73190 enabled persistent cross-site scripting (XSS) and client-side credential skimming at a global scale.
Vulnerability Dissection: Range Header Normalization Asymmetry
The root flaw resided in the edge proxy daemon responsible for handling HTTP multipart byte-range requests destined for Workers KV backends. When a client issues a request with a customized Range: bytes=0-0,-1 header, the edge cache key generation logic normalized the URL path and query parameters but omitted the range specification from the secondary cache key hash.
Furthermore, when the Workers KV origin responded with a 206 Partial Content status accompanied by an ambiguous Content-Range header, the caching layer mistakenly stored the partial byte sequence as the authoritative 200 OK response for full-object requests:
// Malicious Cache-Poisoning Probe:
GET /static/bundle.js HTTP/1.1
Host: api.enterprise-target.com
Range: bytes=0-100, 0-100
X-Custom-Override: malicious_injected_script()

// Edge Response:
HTTP/1.1 206 Partial Content
Content-Range: bytes 0-100/100
CF-Cache-Status: MISS -> Cached as 200 OK for all subsequent clients!
Attack Surface: Global Edge Persistence Without Origin Access
Because Cloudflare’s distributed architecture automatically synchronizes hot cache entries across regional edge clusters, a successful cache poisoning request executed in a single geography could propagate to adjacent points of presence (PoPs):
- Supply Chain Script Injection: By poisoning public JavaScript libraries or payment SDKs served via Workers KV, attackers could execute drive-by Magecart-style form skimming on downstream consumer browsers.
- API Response Hijacking: Poisoning cached JSON responses for authentication endpoints or feature-flag services allowed threat actors to disable security controls or spoof tenant permissions.
- Origin Denial of Service: Crafting corrupted partial chunks caused downstream web applications to fail syntax parsing, crashing client-side web application frontends globally.
Remediation & Edge Hardening Guidance
Cloudflare deployed core proxy updates to ensure that any request containing Range headers is either served directly without caching or partitioned into strictly isolated Range cache shards. Enterprise developers utilizing Cloudflare Workers and Workers KV should execute the following defense steps:
- Purge Edge Cache Namespaces: Perform a comprehensive cache purge on all Worker routes serving dynamic or user-facing assets via the Cloudflare Dashboard or API.
- Explicit Cache-Control Headers: Configure Workers to return
Cache-Control: private, no-transformon endpoints serving sensitive dynamic data or individualized state tokens. - Enforce Subresource Integrity (SRI): Implement SRI cryptographic hashes (
sha384-...) on all script tags loading assets from edge CDNs to ensure client browsers reject poisoned payloads.