 Deep Dive
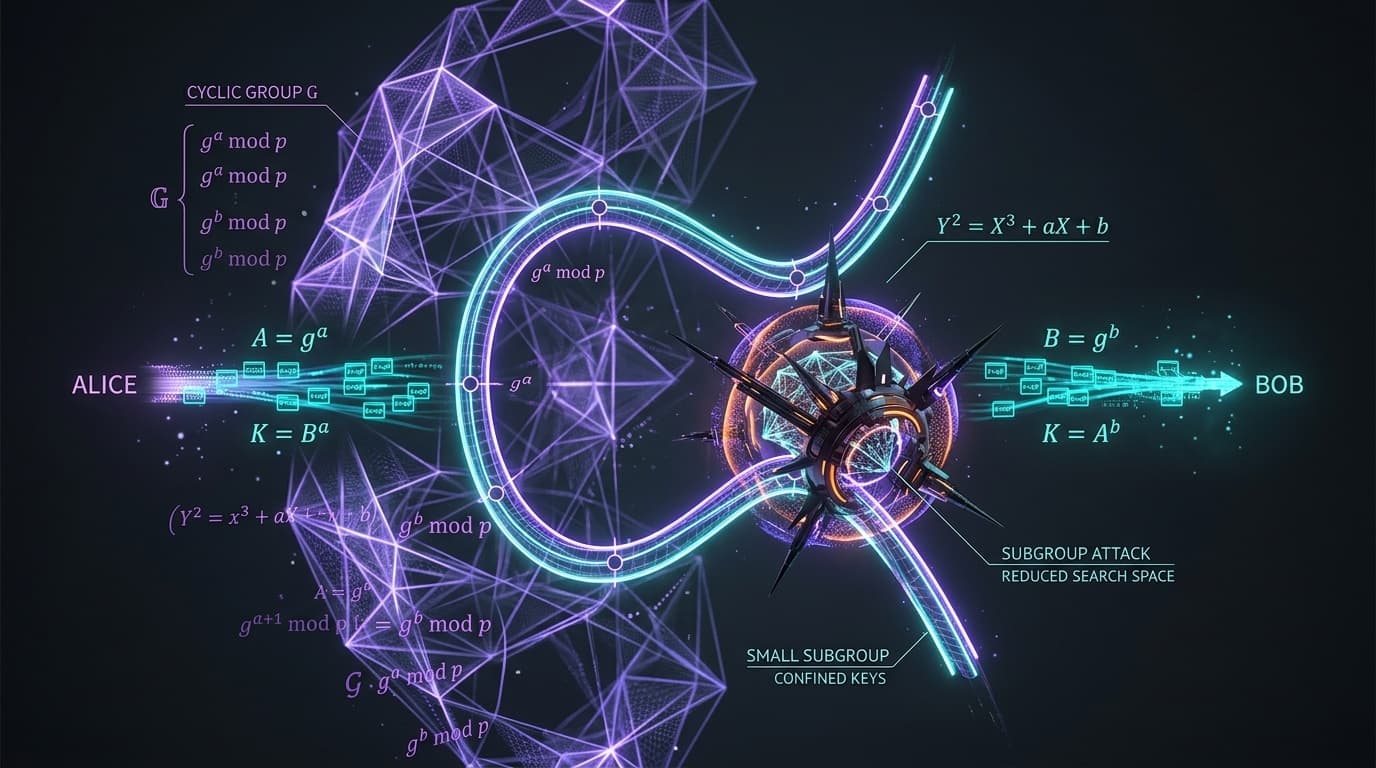
Bouncy Castle C# Vulnerable to Subgroup Confinement Attack Breaking Diffie-Hellman Key Agreement (CVE-2026-63569)
ResearchCloud & SaaSCVE-2026-63569
A critical input validation deficiency in Bouncy Castle C# DHAgreement enables attackers to recover private keys and forge agreed cryptographic values.
Mei-Lin Chen9 min read