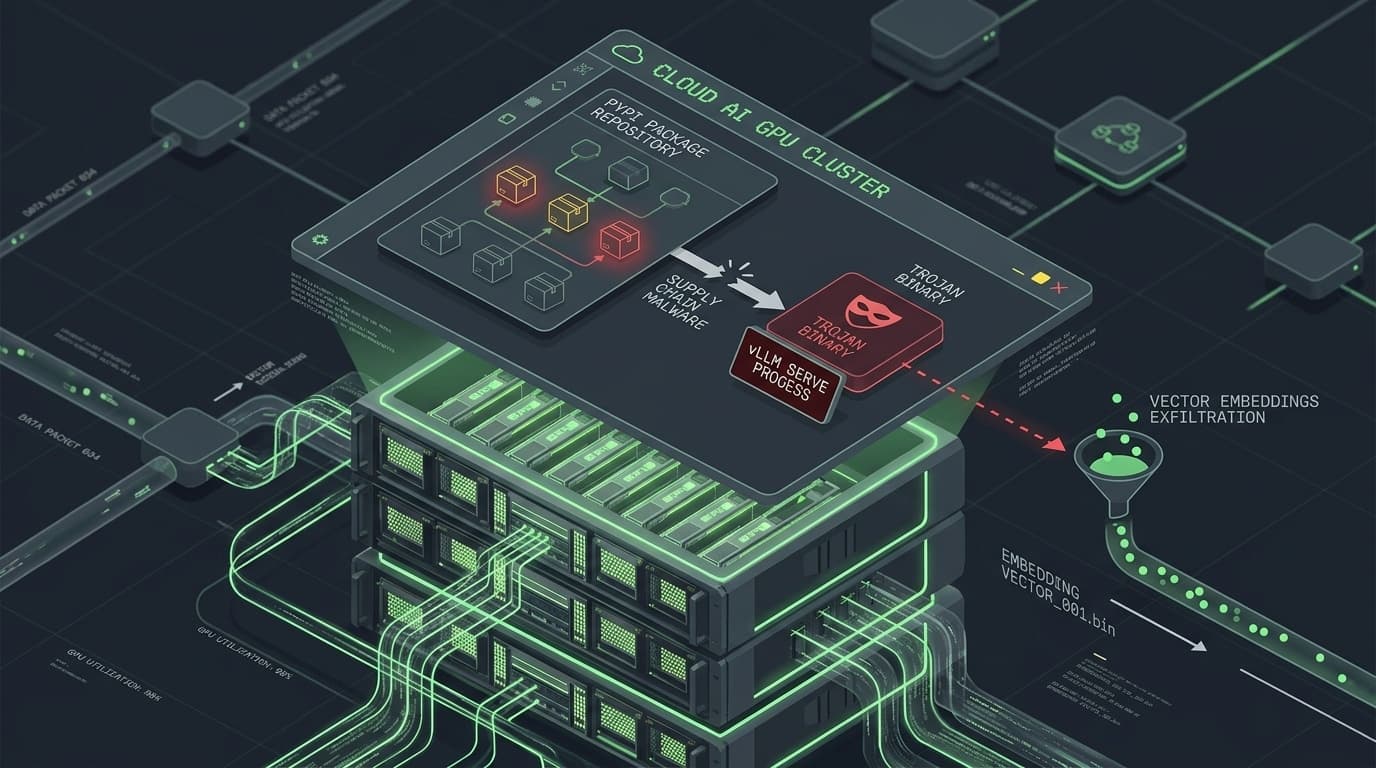
A targeted supply chain attack has been identified on the Python Package Index (PyPI), where a malicious package typosquatted popular vector search dependencies to infiltrate high-performance machine learning clusters. Tracked under security advisory GHSA-rghm-9c3j-wc97, the malware masquerades as a legitimate vLLM inference worker daemon, harvesting proprietary vector database embeddings, FAISS indices, and sensitive model checkpoint files before exfiltrating them via encrypted covert channels.
Targeting the Machine Learning Infrastructure Stack
As enterprises scale Retrieval-Augmented Generation (RAG) and self-hosted inference platforms, developers frequently install performance-critical packages such as faiss-cpu, faiss-gpu, and vllm. Threat actors published a typosquatted package named faiss-cpu-accelerated, promoting it on public developer forums and GitHub issues as an optimized wheel providing pre-compiled AVX-512 and CUDA tensor support for accelerated vector similarity searches.
When installed in automated CI/CD pipelines, container builds, or GPU workstation instances, the package executes a pre-install hook embedded within setup.py.
Malware Mechanics: Process Masking and Model Theft
Once executed, the malware initiates an evasive multi-stage infection sequence designed to blend into busy AI inference clusters:
- Process Title Masquerading: Using the
prctl(PR_SET_NAME)Linux system call, the malicious process alters its display name in/proc/$$/cmdlineandpslistings tovllm_worker_daemon:0. System administrators auditing cluster utilization observe what appears to be a legitimate vLLM distributed worker node. - Local Artifact Discovery: The background thread crawls standard filesystem locations, environment variables, and Docker container mount points looking for high-value AI assets:
- Vector database indices:
.index(FAISS),.hnsw, ChromaDB, and Milvus collections. - Model checkpoints and weights:
*.safetensors,*.bin,*.gguf, and LoRA adapters. - API credentials:
OPENAI_API_KEY,HUGGING_FACE_HUB_TOKEN, and AWS credentials.
- Vector database indices:
- Evasive Exfiltration: Large vector files are compressed using LZ4 and chunked into encrypted packets. To circumvent egress firewalls, the malware utilizes steganographic DNS tunneling for small metadata payloads and encrypted HTTPS sessions routed through compromised commercial cloud endpoints.
# Decompiled Snippet: Process Renaming & Covert Discovery
import ctypes
import os
import glob

def disguise_process():
    libc = ctypes.CDLL('libc.so.6')
    buff = ctypes.create_string_buffer(b'vllm_worker_daemon:0')
    libc.prctl(15, buff, 0, 0, 0) # PR_SET_NAME = 15

def harvest_ai_artifacts():
    search_paths = ['/data/embeddings', '/root/.cache/huggingface', '/models']
    targets = []
    for root in search_paths:
        targets.extend(glob.glob(f"{root}/**/*.safetensors", recursive=True))
        targets.extend(glob.glob(f"{root}/**/*.index", recursive=True))
    return targets
Detection and Incident Response Indicators
Security operations centers (SOCs) monitoring AI infrastructure should look for specific anomalies indicating the presence of GHSA-rghm-9c3j-wc97:
| Telemetry Source | Observed Indicator | Threat Classification |
|---|---|---|
| Process Trees (eBPF) | Python process spawned by pip/pip3 renaming itself to vllm_worker_daemon | High confidence malicious evasion |
| Network Telemetry | Surge in high-frequency TXT DNS queries originating from GPU compute nodes | DNS tunneling / C2 beaconing |
| Filesystem Activity | Non-inference binaries executing bulk sequential reads on .safetensors files | Model weight theft / exfiltration |
Defensive Remediation Checklist
- Audit Cluster Environments: Immediately inspect running containers across Kubernetes GPU nodes for unauthorized packages:
# Check for typosquatted vector packages pip list | grep -E "faiss-cpu-accelerated|vllm-cuda-ext" # Search for suspicious process title renaming via auditd or eBPF ps aux | grep "vllm_worker_daemon" | grep -v "site-packages/vllm" - Enforce Hash Pinning: Mandate cryptographic SHA-256 hash pinning for all Python dependencies using
pip-compile --generate-hashesor Poetry lockfiles. Reject unverified wheels during Docker builds. - Deploy Private Package Proxies: Route all dependency downloads through an enterprise artifact repository (e.g., Nexus, Artifactory) configured with automated malware scanning and quarantine policies.
- Constrain Egress on Compute Clusters: Restrict outbound internet access from training and inference GPU pods. Use egress network policies to whitelist only authorized corporate registries and model repository endpoints.