The cryptocurrency ecosystem has been rocked by the largest digital asset heist in financial history. In late October 2026, threat actors orchestrated a multi-chain raid against the hot wallet infrastructure of Binance, siphoning an estimated $6.3 billion to $6.4 billion in liquid cryptocurrencies and stablecoins across Ethereum, BNB Chain, Arbitrum, and Polygon.
In response to the unprecedented breach, an emergency coalition comprising Binance incident responders, global law enforcement, blockchain analytics firms, and central stablecoin issuers mobilized. Within 48 hours, the alliance executed centralized smart contract blacklisting calls to freeze nearly $3 billion in stolen assets before they could be dispersed into decentralized privacy pools or cross-chain bridges.
Forensic Reconstruction: Hot Wallet Gateway Subversion
According to preliminary technical post-mortems published by Binance and corroborating reports from blockchain intelligence firms Elliptic and TRM Labs, the intrusion did not compromise Binance's cold storage multi-signature vaults, which hold the vast majority of customer collateral. Instead, the attackers achieved persistence within the automated hot wallet disbursement pipeline.
The attack chain involved several sophisticated phases:
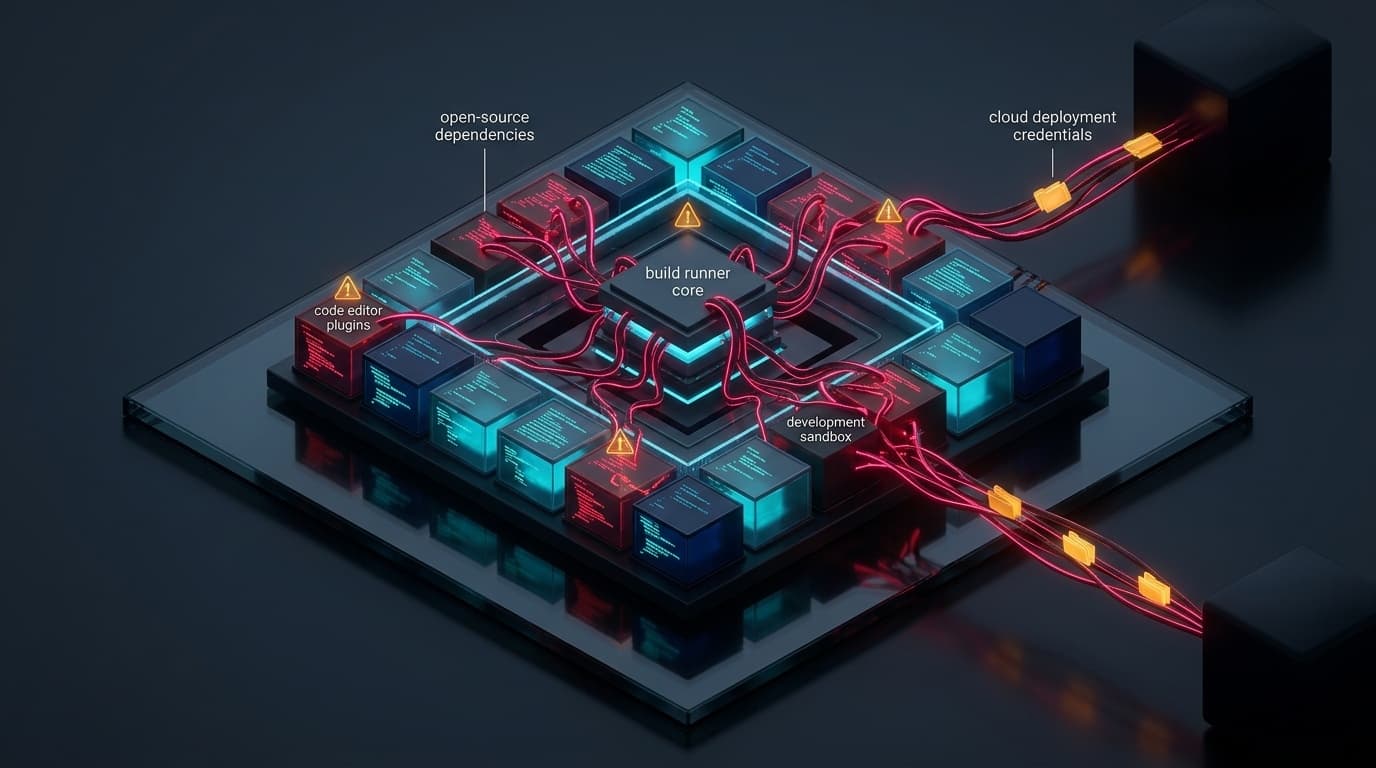
- DevOps Credential Hijacking: Attackers gained initial access through the compromised workstation of an infrastructure engineer, securing administrative tokens for internal Kubernetes clusters that handle transaction queueing.
- RPC Signer Node Manipulation: Rather than stealing private keys in plaintext, the adversaries modified the internal transaction validation logic. This allowed unauthorized automated withdrawal requests to pass internal fraud screening routines without triggering anomaly thresholds.
- Parallel Multi-Chain Drainage: On October 29 at 04:12 UTC, the attackers launched high-concurrency withdrawal batches across dozens of token contracts, rapidly directing liquidity toward freshly initialized intermediary wallets.
Attribution: The Fingerprints of TraderTraitor
Investigators from TRM Labs, Chainalysis, and external threat researchers strongly linked the intrusion to TraderTraitor, an elite cybercrime and espionage collective operating under the command of the Democratic People's Republic of Korea (DPRK) Reconnaissance General Bureau (RGB). The operational signatures closely matched the modus operandi observed in historical multi-hundred-million-dollar exploits against Bybit and the Ronin Bridge:
- Automated token conversion into Ether (ETH) and native assets to evade token-level contract freezes.
- Deployment of bespoke smart contracts configured to fragment large balance transfers into sub-100 ETH increments.
- Rapid routing through decentralized automated market makers (Uniswap, Curve) to dilute transaction trails.
The Great On-Chain Freeze: Centralized Circuit Breakers
Unlike native assets like Bitcoin or Ether, centralized stablecoins possess architectural governance functions that allow token issuers to freeze balances at specific addresses. The rapid mobilization of stablecoin treasuries prevented more than 44% of the exfiltrated loot from reaching unfreezable liquidity pools:
| Issuing Entity / Protocol | Asset Ticker | Total Frozen Value (USD) | Technical Enforcement Mechanism |
|---|---|---|---|
| Tether Limited | USDT | $1.56 Billion | Multi-signature invocation of freeze(address) on smart contracts. |
| Circle Internet Financial | USDC | $800 Million | Invocation of blacklist(address) on ERC-20 token contracts. |
| Arbitrum Security Council | Multi-Token L2 | $380 Million | Emergency DAO multi-sig pause of suspicious bridge exit conduits. |
| Centralized Exchange Coalition | Mixed | $260 Million | Blacklisted incoming deposit clusters across major platforms. |
Binance Balance Sheet & Market Recovery
Binance CEO and executive leadership moved swiftly to reassure the global market, declaring that customer deposits remain 100% whole. The exchange committed its corporate treasury reserves and the $1 billion Secure Asset Fund for Users (SAFU) to cover all net asset shortfalls:
"While this intrusion targeted our operational liquidity, our cold storage vaults were never compromised," Binance stated in its technical incident update. "We have re-keyed all hot wallet signer nodes, implemented hardware-enforced secondary multi-signature thresholds, and replenished over 90% of affected token balances through OTC reserves."
Architectural Lessons for Web3 & Institutional Custodians
The Binance incident serves as a monumental case study for institutional custodians and Web3 developers:
- Decouple Automated Queues from Hot Wallets: Automated withdrawal engines must operate with hard daily value velocity limits enforced at the hardware security module (HSM) level, independent of operating system logic.
- Multi-Party Computation (MPC) with Out-of-Band Quorums: Transaction signing must mandate quorum participation from physically separated devices outside the primary corporate CI/CD and DevOps environment.
- Real-Time Dynamic Blacklisting: Financial protocols must implement automated telemetry feeds capable of pausing gateway bridges within seconds of an anomalous egress surge.